
Agentic AI vs Traditional AI: An Enterprise Autonomy Framework
The useful question in the agentic AI vs traditional AI debate is not which technology is more advanced. It is how much authority a system should have inside a business process. Traditional AI produces a bounded prediction, classification or recommendation. Agentic AI can use models, tools and business systems to decide what happens next – and then move the work forward within defined limits.
That difference changes approval rights, system access, monitoring, accountability and the cost of failure. Start with the workflow and its consequences, not a model shortlist.
This guide focuses on that operating decision. It does not repeat the modelling question covered in our agentic AI vs machine learning guide or the output-versus-action distinction covered in our agentic AI vs generative AI guide. Here, the issue is decision rights: what the system may decide, what it may execute and where a person must remain accountable.
Agentic AI vs traditional AI starts with decision rights
“Traditional AI” is a broad label. In this guide, it means bounded predictive models and conventional automation whose next steps are designed in advance. A model may score a transaction, forecast demand or classify a service request. A person or a preconfigured rule then decides what to do with that output.
Agentic AI adds a control and orchestration layer around one or more models. It can interpret a goal, plan a sequence, choose among approved tools, retain task state and adjust its path as new information appears. Its endpoint is not simply an answer. It is progress toward a completed business outcome.
Consider an IT service request. A traditional model can classify the incident and route it. An agentic system may also inspect recent changes, run an approved diagnostic and apply a low-risk remediation. Both use AI. Only one can advance the workflow.
That leads to a cleaner comparison:
- Primary job: Traditional AI: Predict, classify, score or recommend; Agentic AI: Pursue a goal across multiple steps
- Workflow path: Traditional AI: Designed in advance; Agentic AI: Selected within allowed paths as evidence changes
- System access: Traditional AI: Usually read-only or narrowly integrated; Agentic AI: Uses tools and systems through scoped permissions
- Human role: Traditional AI: Interprets or acts on the output; Agentic AI: Defines authority, approves exceptions and supervises outcomes
- Main risk: Traditional AI: An inaccurate output; Agentic AI: An inaccurate action or a sequence of compounding actions
- Success measure: Traditional AI: Model quality and decision usefulness; Agentic AI: Completed outcomes, intervention rate, cost and control performance
The practical boundary is authority. If the system stops after informing a person, it remains decision support. If it executes the next step, the organisation has delegated a decision right – and needs matching controls.
The autonomy ladder is more useful than a binary choice
Enterprise teams often frame adoption as manual work on one side and full autonomy on the other. That creates unnecessary risk. Autonomy is better designed as a ladder, with a different control model at each level.
- Assist: The system retrieves, summarises or drafts. A person performs every business action.
- Recommend: The system proposes a decision and explains the evidence. A person accepts, changes or rejects it.
- Act with approval: The system prepares an action but cannot execute until an authorised person approves it.
- Act within limits: The system completes low-risk actions independently and escalates exceptions or threshold breaches.
- Pursue a bounded goal: The system plans and executes several approved steps, while remaining constrained by permissions, budgets, stopping conditions and audit requirements.
This ladder turns a vague technology discussion into an operating-model decision. A service agent might independently reset a password, require approval to change access rights and only recommend actions during a suspected security incident. The level should vary by action consequence.
This is also why “human in the loop” is not a complete governance strategy. Leaders must specify which human, at what point, with what evidence and within what response time. An approval gate that no named role owns is simply a queue where automation goes to stall.
Agentic AI vs traditional AI changes the control surface
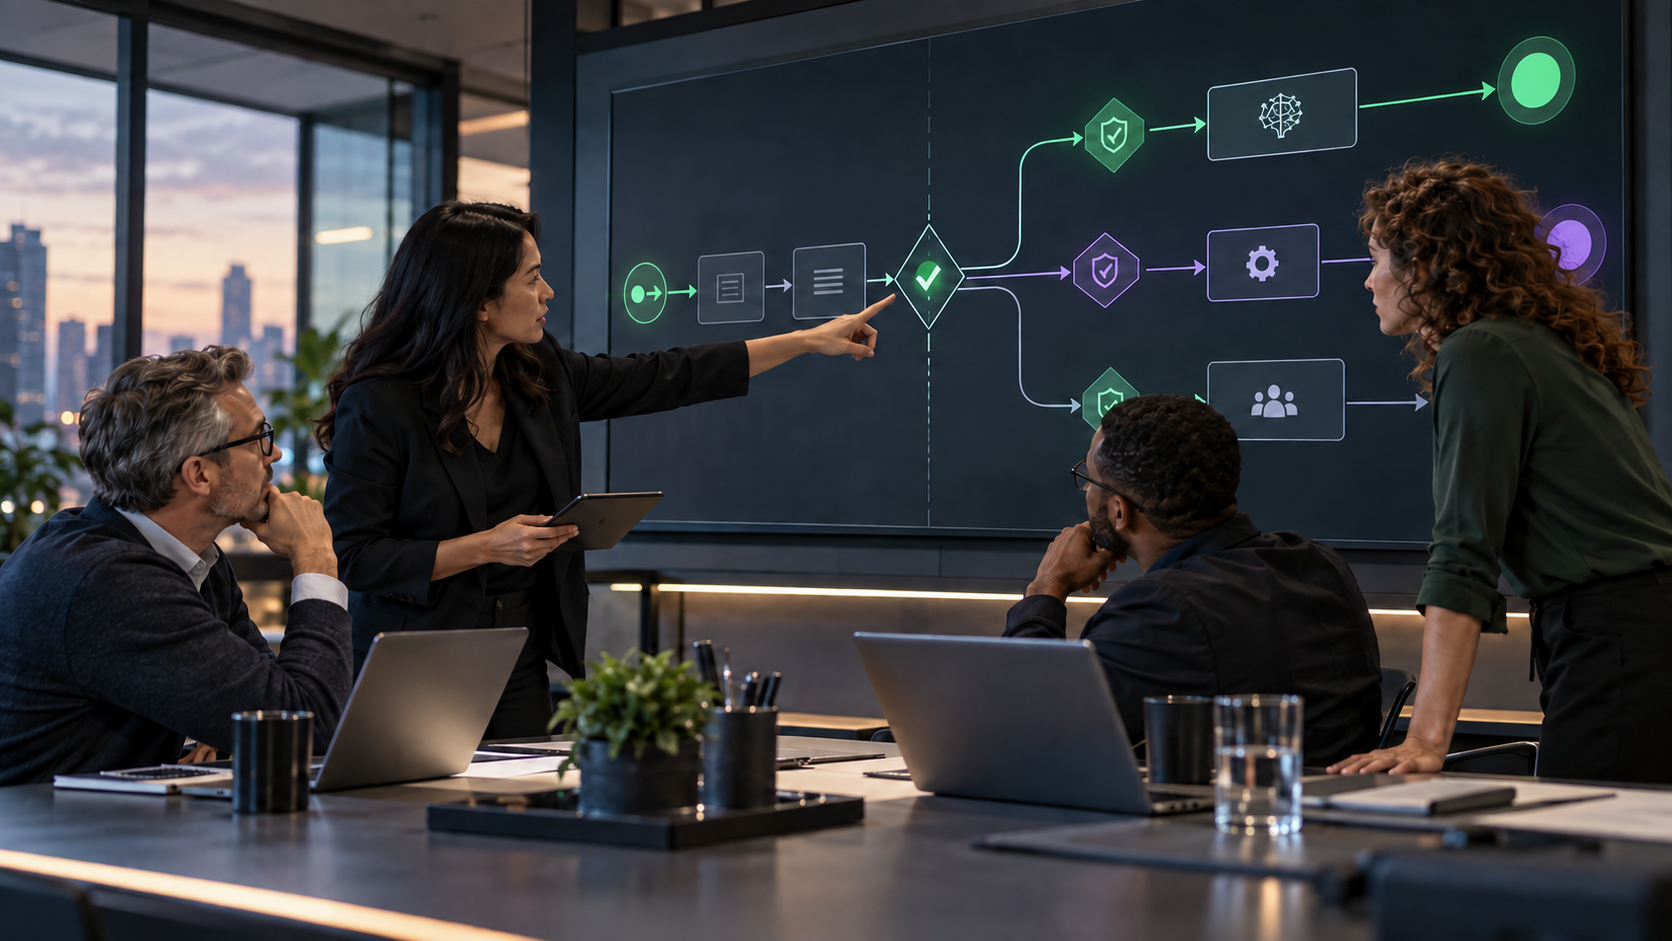
Traditional AI governance usually concentrates on data quality, model performance, drift, bias, privacy and explainability. Those controls remain necessary in an agentic system, but they are no longer sufficient. Once software can act, governance must extend from the model to the full execution path.
A production-grade control surface covers six areas:
- Identity: Every agent and delegated user context must be identifiable. Shared credentials make accountability impossible.
- Permissions: Read, recommend and write access should be separated. Each tool should expose only the operations and records required for the task.
- Boundaries: Step limits, time limits, transaction thresholds and spending budgets prevent an open-ended plan from becoming an open-ended liability.
- Evidence: The system should retain the inputs, tool calls, decisions, approvals and outputs needed to reconstruct what happened.
- Evaluation: Teams need scenario tests for expected work, edge cases, adversarial inputs, tool failure and escalation – not just a sample of well-written responses.
- Recovery: Consequential actions need a defined way to stop, reverse, compensate or hand off when the system is uncertain.
This control surface separates a compelling demonstration from a dependable production service. A model may appear capable while the enterprise remains unprepared to grant it identity, tool access or authority. The constraint is often the absence of a safe operating envelope.
Risk compounds when decisions become actions
A wrong prediction is usually a local event. A wrong action can change the state of another system, and every later step may inherit that altered state. Agentic risk therefore compounds across a sequence.
In procurement, a traditional model might flag an inventory shortage for review. An agentic system could verify stock, compare approved suppliers and prepare a purchase request. If it misreads a unit of measure, that error can influence every later step.
The answer is to contain errors with narrow tools, verified data, deterministic checks and approval gates before irreversible actions. Confidence in an answer is not authority to act.
For every action, ask four questions:
- What is the maximum impact if this action is wrong?
- Can the action be reversed completely and quickly?
- Will another control detect the error before harm occurs?
- Who owns the exception when the system stops?
If those answers are unclear, the workflow is not ready for higher autonomy – even if the model performs well in a pilot.
A six-gate framework for choosing the right model
Use the following gates before deciding where agentic AI belongs. A “no” does not necessarily end the initiative; it usually identifies the work required before more authority is granted.
1. Is the outcome clear?
Define success as a completed business outcome. “Use an agent for service operations” is vague. “Resolve eligible access requests within policy, with an auditable record and no increase in security exceptions” is testable.
2. Does the path vary?
If the same input always follows the same steps, conventional automation may be faster and easier to control. Agentic AI earns its complexity where the goal is stable but the path changes.
3. Are the actions bounded and reversible?
Classify every permitted tool action by consequence. Start with read access and reversible actions. Add write access only when approvals, limits and recovery are explicit.
4. Are the systems ready?
Agents depend on reliable APIs, usable identity controls, trusted data and clear system ownership. If employees complete the process through undocumented workarounds, an agent will inherit the same fragility at machine speed.
5. Can performance be observed end to end?
Track task completion, escalation, overrides, cost, policy compliance and post-action defects. A team that cannot see the full path cannot manage the full risk.
6. Does the value justify the control burden?
Compare orchestration, integration, evaluation and adoption costs with the value of the completed workflow. High-volume, multi-step work with costly coordination is a strong candidate.
- One bounded prediction or classification: Recommended starting point: Traditional AI
- Fixed sequence with stable rules: Recommended starting point: Conventional automation, with AI where useful
- Variable sequence; actions remain reversible: Recommended starting point: Agentic AI with bounded tool access
- Consequential action with clear approval ownership: Recommended starting point: Agentic AI with an approval gate
- Unclear data, permissions or process ownership: Recommended starting point: Fix the foundation before adding autonomy
- Stable core with variable exceptions: Recommended starting point: Hybrid architecture
The strongest enterprise architecture is usually hybrid
Most production systems should not force every part of a workflow into one pattern. A hybrid architecture assigns each job to the simplest reliable mechanism.
Deterministic rules are appropriate for hard policy constraints. Predictive models are appropriate for scoring, forecasting and classification. Generative models are appropriate for interpreting unstructured information and preparing language. Agentic orchestration is appropriate for coordinating variable steps across tools. People remain accountable for ambiguous, sensitive or high-consequence decisions.
In customer service, a classifier can identify intent, retrieval can provide approved policy, a generative model can prepare a response and an agent can coordinate permitted next steps. Low-value refunds may be automatic; exceptions require approval.
This also improves economics. Deterministic components handle predictable work, model reasoning is reserved for genuine variability and approval effort is concentrated on exceptions.
How to introduce autonomy without redesigning everything at once
Start with one workflow whose value and boundaries are visible. Map its workarounds, approvals and failure paths, then baseline cycle time, manual effort, errors and exceptions.
Then grant autonomy in stages:
- Deploy the system in observation mode and compare its proposed actions with real outcomes.
- Allow it to recommend while people approve every action.
- Automate a small set of reversible, low-risk actions under explicit thresholds.
- Expand only when completion, override, cost and control metrics remain within agreed limits.
This sequence creates evidence for each additional decision right and exposes weaknesses before the system can act on them. The goal is the highest useful autonomy the organisation can govern with confidence.
What this means for your AI strategy
The agentic AI vs traditional AI decision is ultimately a question of operating authority. Traditional AI remains the right choice for bounded analysis, prediction and recommendation. Agentic AI becomes valuable when work spans systems, the path varies and completing the outcome matters more than producing another insight.
Enterprise leaders should therefore begin with the action, its consequence and its owner. Choose the simplest architecture that completes the job. Increase autonomy only when permissions, evidence, recovery and economics support it. In many cases, the best design combines rules, predictive AI, generative AI, agentic orchestration and human judgment in one controlled workflow.
Softobiz helps enterprise teams identify high-value workflows, define autonomy boundaries and engineer governed agentic systems from pilot to production. Talk to our AI engineering team about the operating model that fits your environment.
Frequently asked questions
What is the main difference between agentic AI and traditional AI?
Traditional AI produces a bounded output such as a prediction, score or classification. Agentic AI can use approved tools and systems to select and execute the next steps toward a goal. The main difference is delegated authority, not simply model capability.
Does agentic AI replace traditional AI?
No. Agentic systems often use traditional predictive models for specific tasks. The agentic layer coordinates those components and advances the workflow. A hybrid design is usually more reliable and economical than attempting to make every component agentic.
Which workflows should become agentic first?
Start with high-volume workflows that span systems, contain bounded variability and use reversible actions. Avoid poorly understood processes or irreversible, high-consequence decisions.
How much human oversight does an AI agent need?
Oversight should match the consequence of each action. Low-risk, reversible steps may run independently. Sensitive, unusual or high-value actions should require approval or escalation to a named owner with enough evidence to decide.
How should leaders measure an agentic AI system?
Measure completed outcomes, cycle time, cost per completed task, escalation and override rates, policy compliance, tool failures and post-action defects. Model accuracy alone cannot show whether the workflow is safe or valuable.